Back to Blogcyber-security-patterns 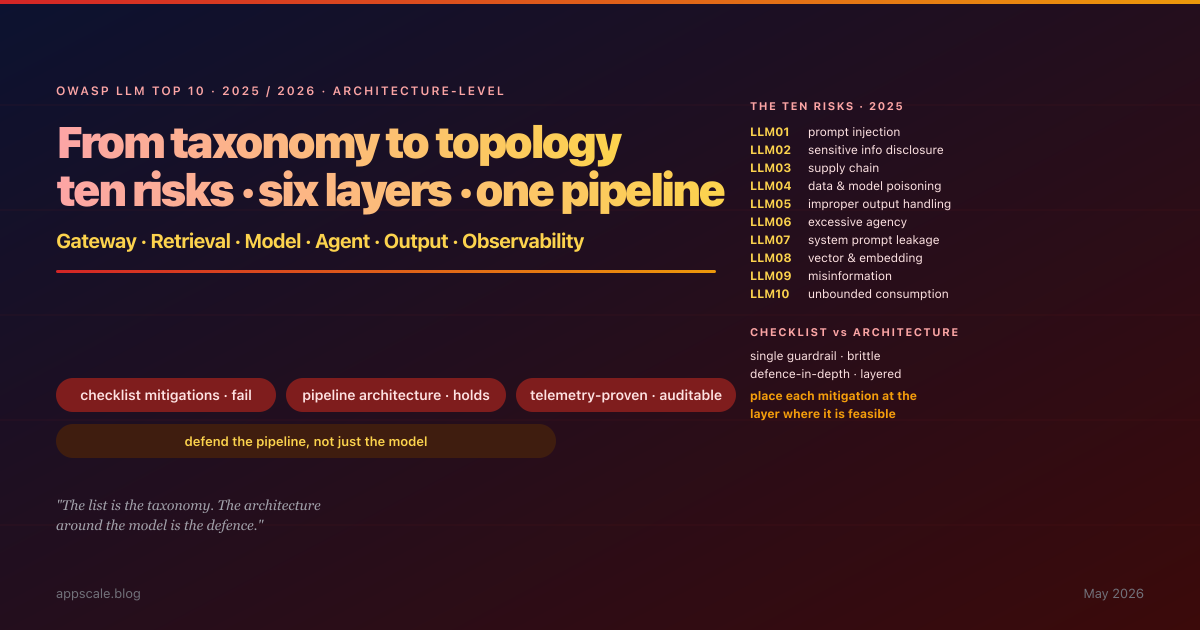
OWASP LLM Top 10 (2025/2026): Architecture-Level Mitigations Mapped to Each Risk
owasp llm top 10 owasp 2025 llm security ai security architecture prompt injection defence sensitive information disclosure llm supply chain model poisoning data poisoning improper output handling excessive agency system prompt leakage vector database security embedding security rag security misinformation llm unbounded consumption llm llm gateway security defence in depth llm capability tokens agent human in the loop cyber security patterns evergreen 2026